Why Government Data Breach Prevention Starts at End of Life, Not Day One
Most agency security programs pour resources into the front end of the asset lifecycle. Procurement controls, configuration baselines, endpoint protection, identity and access management, network segmentation. All necessary, all important. But here is the gap most security leaders underinvest in: what happens to the data on a device the day after it gets retired. Government data breach prevention is incomplete if it stops at the day a laptop comes out of service. Every retired drive that still holds recoverable data is an unsecured copy of whatever sensitive information sat on it, and unlike an active endpoint, nobody is monitoring it. According to IBM’s 2025 Cost of a Data Breach Report, U.S. data breaches now average $10.22 million per incident, more than double the $4.88 million global average. A meaningful share of those incidents trace back to disposal, storage, and chain of custody failures, not active intrusions.
Why Are Public Sector Breaches So Expensive?
Several reasons compound. Government agencies hold high value data: citizen PII, tax records, benefits information, law enforcement records, health data, and in many cases CUI or classified information. The regulatory and oversight environment is dense, which means a breach triggers reporting to CISA, the inspector general, possibly Congress, and depending on the data, state attorneys general or the affected individuals. The reputational cost is its own category. Agencies operate on public trust, and when that trust takes a hit, the downstream consequences ripple through everything from program participation to legislative support to staff morale. Government data breach prevention is not just a security investment, it is an investment in the agency’s ability to do its mission.
What Are the Most Common ITAD Breach Vectors in Government?
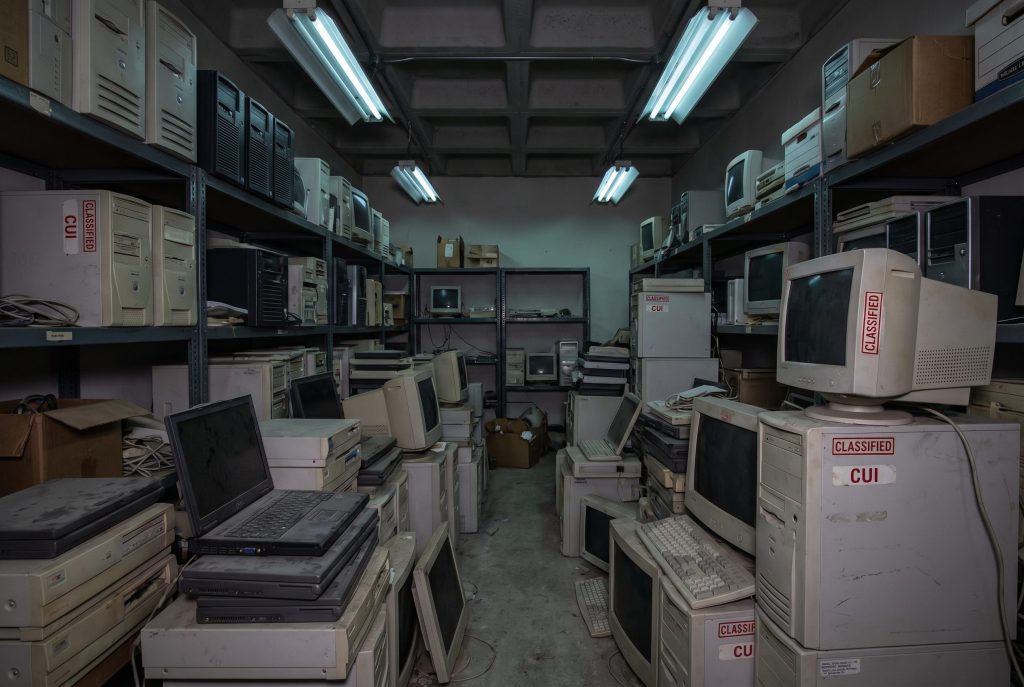
Four show up over and over in inspector general findings and GAO reports. The first is stockpiling: retired hardware sitting in storage rooms, warehouses, and field offices for months or years before disposal, with no real access controls and no inventory of what data is on which device. The second is reliance on factory reset or basic reformatting, both of which leave data fully recoverable with off the shelf forensic tools. The third is improper handling of solid state media. Standard overwrite procedures do not adequately sanitize SSDs, NVMe drives, or embedded flash, and many agencies are still treating them like spinning magnetic drives. The fourth is uncertified vendors, where agencies hand off equipment to whoever has the lowest bid without verifying R2v3, NAID AAA, ISO 27001, or where applicable GSA approval and NSA EPL compliance for classified work.
How Do You Quantify the Risk Before a Breach Forces You To?
Start with an honest inventory. Walk every storage location your agency uses and count every retired asset that still contains data. Classify each one by the highest data sensitivity it ever processed, because forensic recovery does not care that the data was supposed to have been deleted. Multiply that count by the realistic exposure per asset. For an agency holding citizen PII, regulated health data, or financial records, the exposure per record can run from tens to thousands of dollars depending on the data type. For CUI or classified data, the exposure is no longer measurable in dollars alone, it is measurable in mission impact. That number, even at conservative assumptions, will almost always dwarf the cost of running a proper Government ITAD program. The math here is rarely close.
What Controls Actually Move the Needle on Government Data Breach Prevention?
Five controls do the heavy lifting. First, eliminate stockpiling by setting a maximum dwell time for retired assets, ideally measured in weeks, not quarters. Second, enforce sanitization at the source by sanitizing or queuing for sanitization the moment an asset comes out of service, not when someone gets around to it. Third, match sanitization method to data sensitivity using NIST SP 800-88 Rev. 2 (Clear, Purge, or Destroy), and use IEEE 2883 compliant tools for solid state media. Fourth, require serial number level chain of custody for every asset from desk to final disposition. Fifth, vet your vendors against current certifications and require asset level certificates of sanitization or destruction, not aggregate summaries. None of this is exotic. All of it is well within reach of any agency that decides to take government data breach prevention at end of life as seriously as it takes intrusion detection at the perimeter.
How Should You Choose a Vendor That Actually Reduces Breach Risk?
Treat vendor selection like the security control it is. Require current R2v3 certification (not the outdated R2:2013), NAID AAA for data destruction, ISO 27001 for information security management, and ISO 14001 for environmental management. For federal work, look for GSA approval and, where applicable, certification through the Defense Logistics Agency. For classified work, require NSA EPL listed equipment matched to the media type. Verify certifications independently through the SERI R2 directory and the NAID certified company directory, not just the vendor’s own marketing. Ask hard questions. Where does the equipment physically go? Who handles it at every step? Can you provide witnessed destruction? What does your certificate of sanitization actually show? Can I see a sample audit package? A vendor that fumbles those answers is a breach waiting to happen.
So Why Should Your Agency Treat ITAD as a Core Government Data Breach Prevention Control?
Because it is one of the few breach vectors that is almost entirely within your agency’s control. Nation state actors, sophisticated phishing campaigns, supply chain compromises, zero day exploits, those threats are real and require ongoing investment, but you cannot eliminate them. Improper IT asset disposal is different. The drives are sitting in your buildings. The data is on your hardware. The decision about how to sanitize, document, and verify destruction is entirely yours. With U.S. data breaches now averaging $10.22 million per incident, the cost of a single ITAD related disclosure dwarfs what a defensible program costs to run. Government data breach prevention through proper ITAD comes down to the same five things: cap dwell time on retired assets, sanitize at the source, match method to sensitivity using NIST SP 800-88 Rev. 2, document at the serial number level, and use vendors with current certifications and verifiable evidence. Do that consistently and you close one of the most preventable breach vectors in the public sector. That is the foundation, and everything else builds from there.