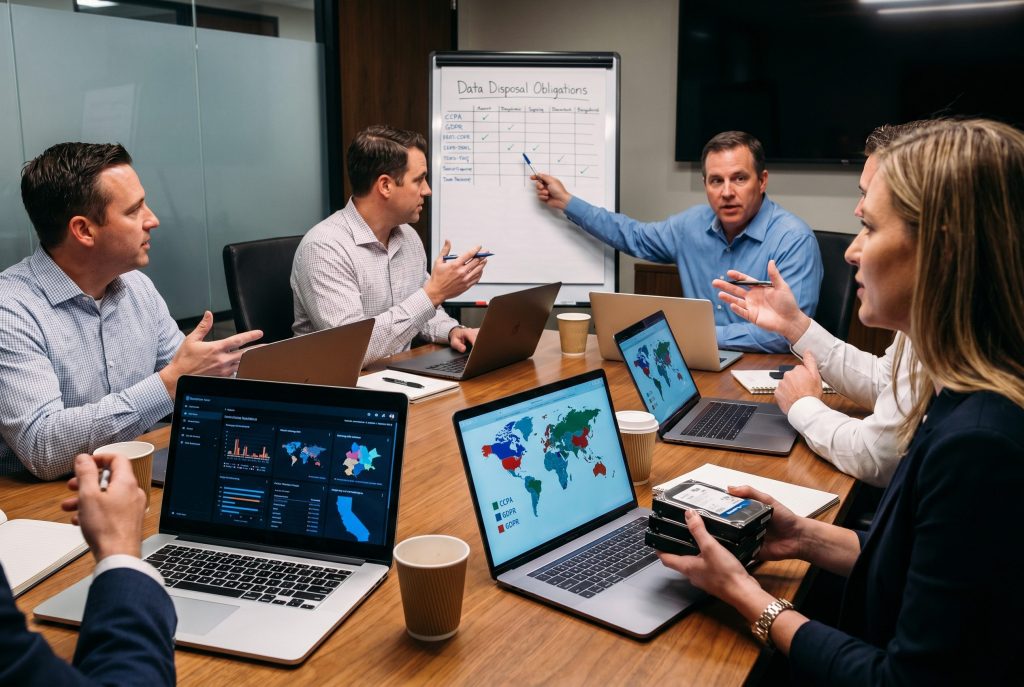
Why Data Privacy Laws Make Business ITAD a Compliance Requirement, Not a Suggestion
If your company collects customer names, email addresses, payment information, Social Security numbers, or any form of personally identifiable information, you are subject to data disposal obligations whether you realize it or not. The idea that data privacy regulations only apply to hospitals, banks, and government agencies is one of the most expensive misconceptions in business today.
As of 2026, 19 states have comprehensive consumer privacy laws in effect, and every one of them creates obligations around how businesses handle, retain, and ultimately destroy personal data. Business ITAD is the operational process that fulfills those obligations at end of life. Skip it, and you are not just leaving data on old drives, you are leaving your company exposed to enforcement actions, private lawsuits, and breach costs that can run into the millions.
What Does the CCPA Actually Require When You Retire Old Equipment?
The California Consumer Privacy Act, as amended by the CPRA, gives consumers the right to request deletion of their personal information, and businesses must fulfill that request within 45 days. That obligation extends to service providers, contractors, and data sharing partners, creating a chain of deletion responsibility. Most businesses think about deletion in terms of databases and cloud systems.
They forget about the laptop in the storage room that still has a local copy of the customer file, or the backup tape sitting in a box nobody has touched in two years, or the multifunction printer with an internal hard drive that cached every document it ever scanned. Under the CCPA, if recoverable consumer data exists on retired equipment, it is still your problem. CCPA penalties reach $2,500 per negligent violation and $7,500 per intentional violation, per record. The law also creates a private right of action for data breaches resulting from a business’s failure to implement reasonable security, with statutory damages between $100 and $750 per consumer per incident. A stack of unwiped laptops in a closet is exactly the kind of “failure to implement reasonable security” that triggers that liability.
How Many State Privacy Laws Apply to Your Business Right Now?
More than most companies have accounted for. As of early 2026, 19 states have active comprehensive privacy laws: California, Colorado, Connecticut, Delaware, Indiana, Iowa, Kentucky, Maryland, Minnesota, Montana, Nebraska, New Hampshire, New Jersey, Oregon, Rhode Island, Tennessee, Texas, Utah, and Virginia. If your business sells products or services to residents in any of those states, or if you process personal data from consumers in those states, you are likely covered.
Penalties vary by state but follow a pattern. Indiana and Kentucky allow up to $7,500 per violation. Rhode Island goes up to $10,000 per violation with no cure period, meaning you face penalties immediately with no opportunity to fix the issue first. Texas secured a settlement of over $1 billion against a major technology company in 2025, setting a precedent that smaller businesses should not ignore. The takeaway for business ITAD is direct: every one of these laws creates an implicit obligation to destroy personal data when it is no longer needed, and that includes data sitting on hardware you have already stopped using.
What About PCI DSS, SOX, and GDPR?
If your business handles payment card data, PCI DSS Requirement 3 mandates that cardholder data be rendered unrecoverable when it is no longer needed for business, legal, or regulatory purposes. That applies to every device that ever processed, stored, or transmitted cardholder data, including point of sale terminals, servers, and workstations. If your company is publicly traded, SOX compliance requires controls over the integrity of financial records throughout their lifecycle, including disposal.
An auditor finding that financial data was recoverable from improperly disposed hardware is the kind of control weakness that makes it into the audit report. If you do business with EU residents, GDPR’s right to erasure (Article 17) requires you to erase personal data when it is no longer necessary for its original purpose, and fines can reach 4% of global annual revenue or 20 million euros, whichever is higher. Each of these frameworks points to the same operational requirement: a documented, verifiable business ITAD process that proves data was properly destroyed.
What Documentation Do You Need to Stay Audit Ready?
Three things, regardless of which regulations apply to you. First, a written policy that defines how your company handles IT asset disposition, including roles, responsibilities, and the sanitization methods you use mapped to data sensitivity. Second, a procedure document or SOP that describes the operational workflow from the moment a device comes out of service to its final disposition.
Third, asset level evidence: certificates of sanitization or destruction tied to specific serial numbers, listing the method used, the standard followed, the operator, the date, and the validation result. A tool like Blancco Drive Eraser generates tamper proof certificates of erasure that serve exactly this purpose. If your ITAD vendor can only give you a batch summary that says “200 drives destroyed,” you do not have audit ready evidence. You have a marketing document.
So Do Privacy Laws Really Create the Same Data Liability for Businesses as Regulated Industries?
Yes. The moment your business stores a customer’s personal information on a device, you carry a disposal obligation that mirrors what hospitals face under HIPAA and what banks face under GLBA, even if you are a midsize e-commerce company or a regional services firm. The CCPA does not distinguish between a hospital and a retailer when it comes to deletion rights.
State privacy laws do not care whether you think of yourself as a “regulated” business. And when a breach traces back to a retired laptop that was never wiped, the penalties, the lawsuits, and the reputational damage hit the same regardless of your industry. Business ITAD is the process that closes that gap. Document your policy. Match sanitization to data sensitivity. Require serial number level evidence from your vendor. Treat disposal as the compliance control it is, not the afterthought most companies still assume it to be. That is the foundation, and everything else builds from there.lse builds from there.